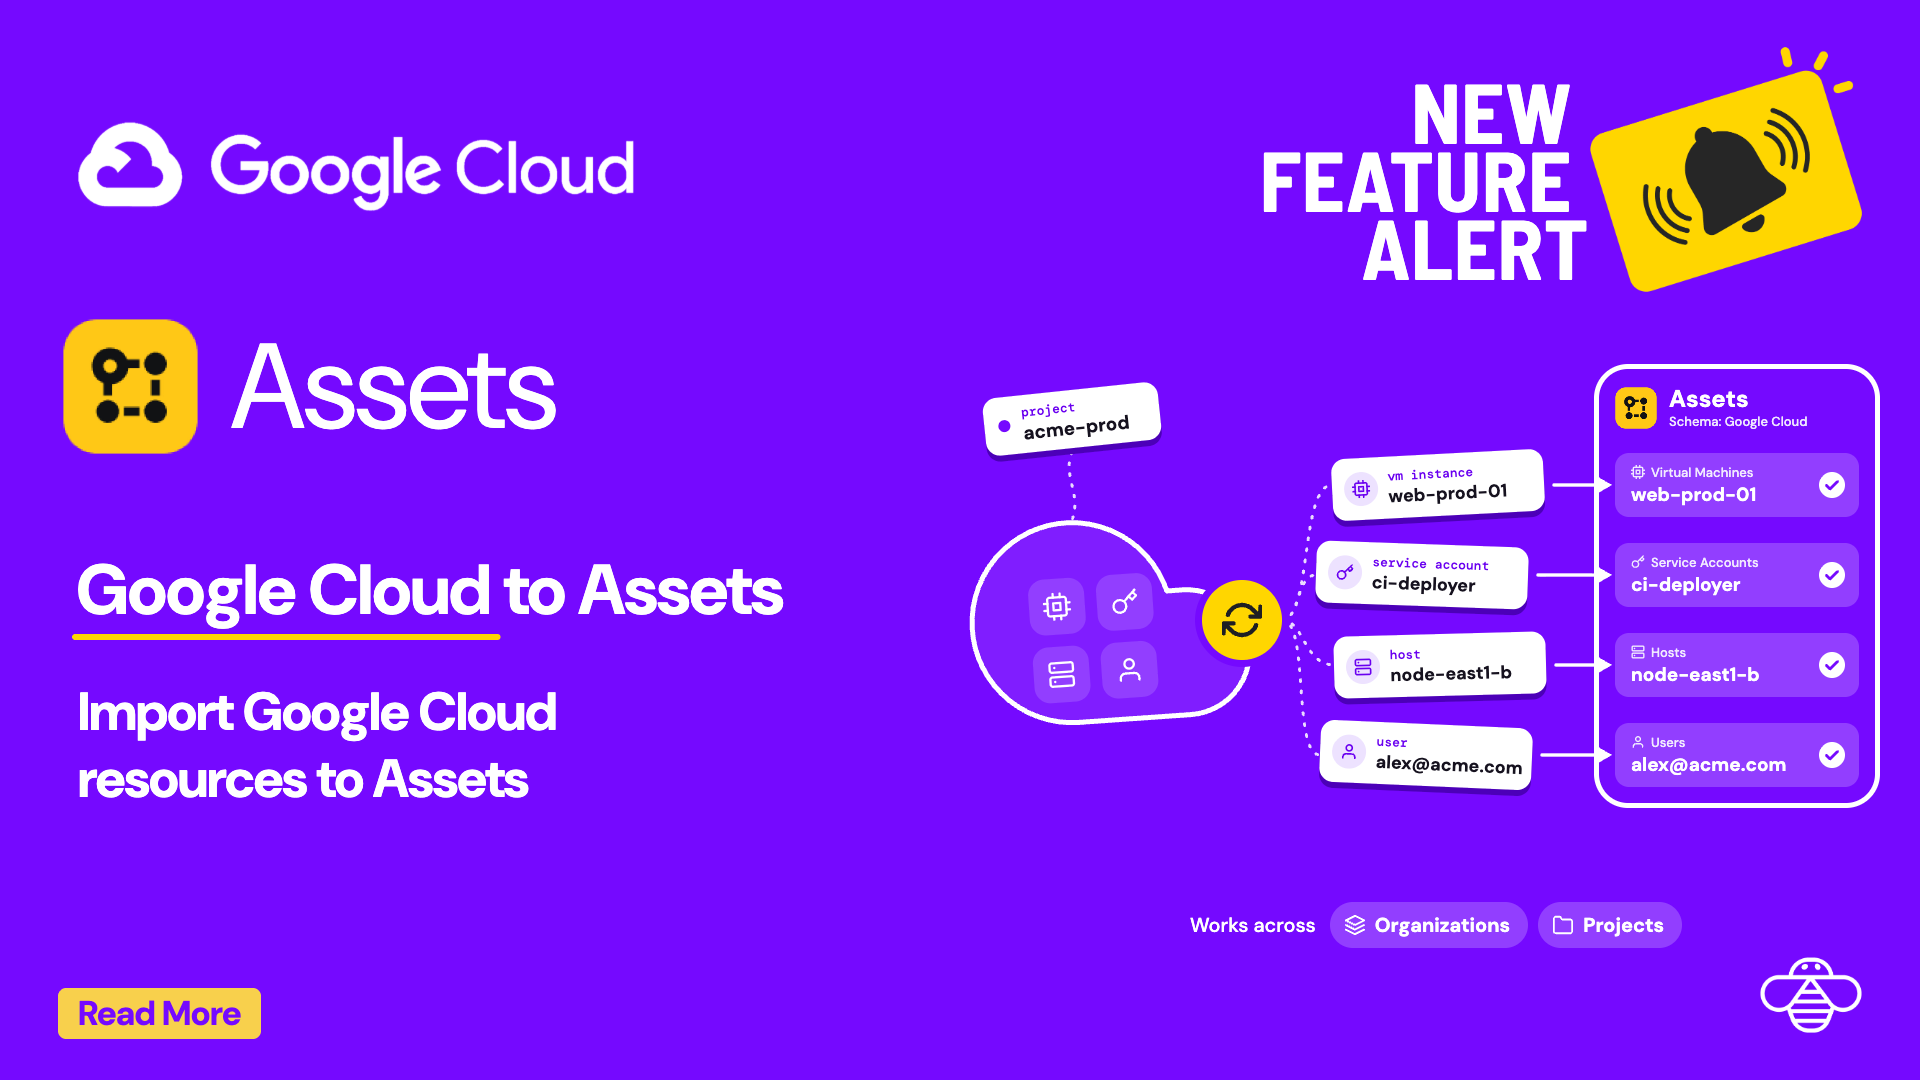
This article shows how to import Google Cloud resources into Assets.
Why put Google Cloud resources in Assets
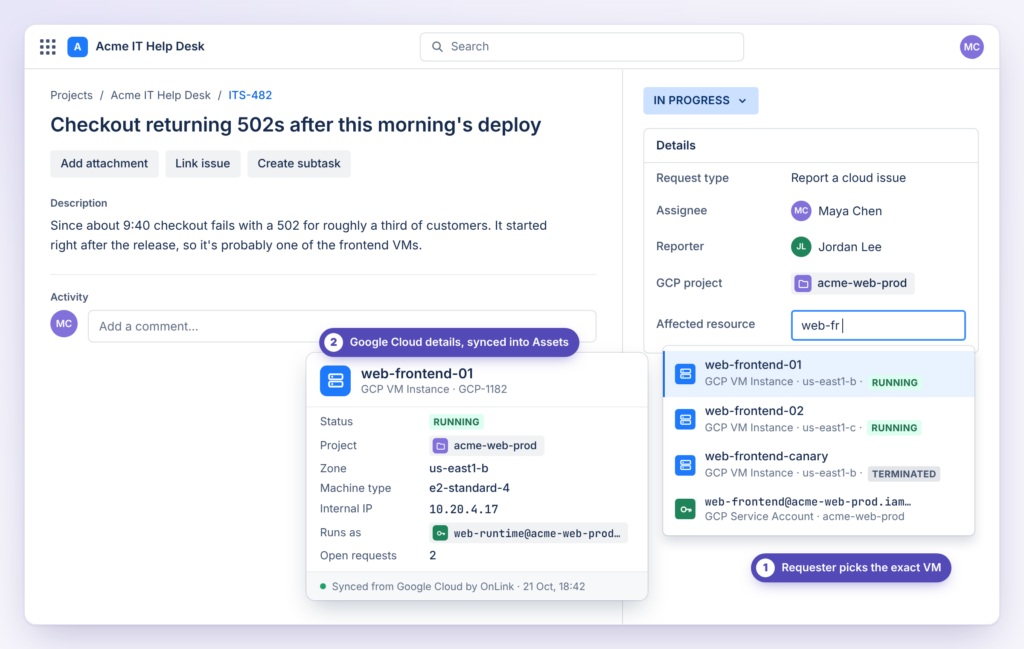
Requesters pick, not describe. An Assets field on the request form lists your real VMs, projects and service accounts.
Agents get context without console access. Project, zone, status, internal IP and the service account a VM runs as are on the ticket.
History per resource. Every incident, change and access request links to the VM or service account it touched.
One CMDB. Google Cloud resources sit next to the laptops, phones and people you already sync into Assets.
What it looks like
The requester types part of a VM name into an Assets field and picks the exact resource. The agent sees where it runs, what it runs as, and what else is open against it.
Example data. Field names and attributes depend on how you set up your object schema.
Google Cloud authentication
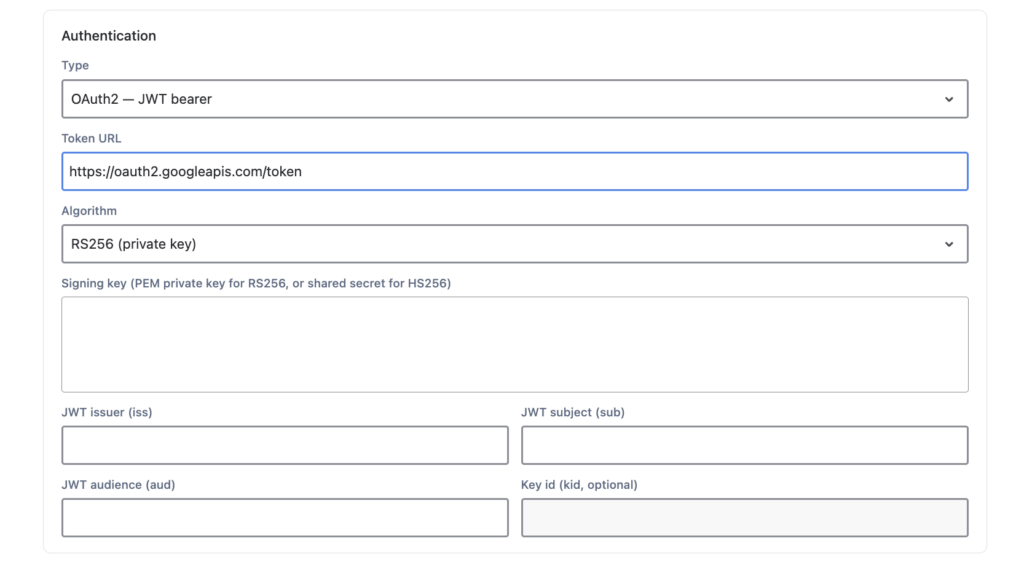
OnLink signs in as a Google Cloud service account. It signs a JWT with the account’s private key and exchanges it for a short-lived OAuth access token.
In an admin project, enable the Cloud Asset API.
Create a service account, for example onlink-assets-sync.
On the organization (not a project), grant it Cloud Asset Viewer (roles/cloudasset.viewer). It is read-only.
On the service account’s Keys tab, create a JSON key.
In OnLink, enter client_email, private_key_id and private_key from the key file. Use the token URL https://oauth2.googleapis.com/token and the scope https://www.googleapis.com/auth/cloud-platform.
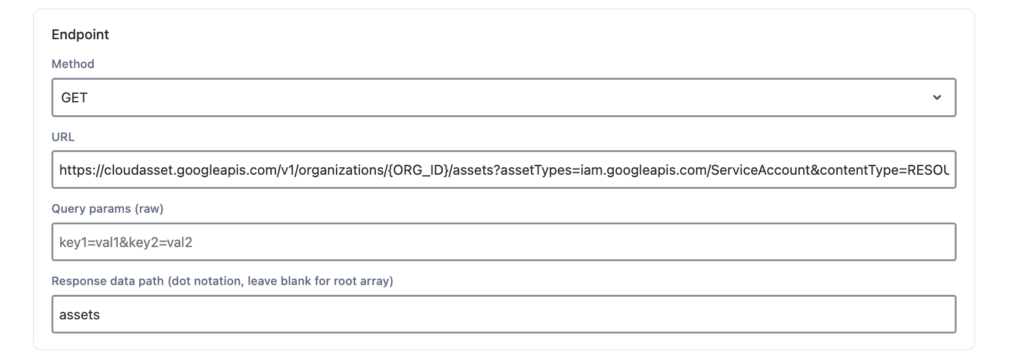
Use Cloud Asset Inventory’s assets.list. One paged request returns every VM in the organization, across all projects and zones, so you don’t loop through projects with the Compute API.
GET https://cloudasset.googleapis.com/v1/organizations/{ORG_ID}/assets?assetTypes=compute.googleapis.com/Instance&contentType=RESOURCE&pageSize=1000
Setting
Value
Response data path
assets
contentType
RESOURCE, so each record includes the full VM in resource.data
pageSize
1000, the maximum
Pagination
Read nextPageToken from the response and send it back as pageToken
For service accounts, keep the same request and change assetTypes to iam.googleapis.com/ServiceAccount.
OnLink mapping
Sample Service Account Mapping. Refer to documentation for VM Mapping.
This guide explains how to use OnLink to import Google Cloud resources into JSM Assets, so anyone raising a JSM request can pick the affected project, VM or service account. It covers Google Cloud authentication, the API request, sample data, pagination, field mapping, validation, and import execution.
key:name=Resource Name
map:resource.data.email=Email
map:resource.data.displayName=Display Name
map:resource.data.uniqueId=Unique ID
map:resource.data.projectId=Project ID
map:resource.data.description=Description
map:updateTime=Last Changed
Import projects and service accounts before VMs so the two references have something to point at. create=false stops the VM import from creating placeholder objects. Full field-by-field tables for VMs and service accounts are in the setup guide.
Try OnLink
OnLink is a Cloud Fortified app that brings 100+ sources into JSM Assets: HR systems, identity providers, MDMs, and now Google Cloud.
Can I sync one project instead of the whole organization? Yes. Change the URL scope from organizations/{ORG_ID} to projects/{PROJECT_ID}, and grant Cloud Asset Viewer on that project.
Does OnLink need write access to Google Cloud? No. Cloud Asset Viewer is read-only. The cloud-platform scope sounds broad, but what the service account can do comes from its IAM roles.
Can I use a client ID and secret instead of a key file? No. Google doesn’t offer a client-credentials grant for its APIs. Servers use a service account and a signed JWT. A user sign-in works, but it breaks whenever your admin’s Google Cloud session length runs out.
Our organization blocks service account keys. Now what? Organizations created on or after May 3, 2024 enforce iam.managed.disableServiceAccountKeyCreation by default. Ask an Organization Policy Administrator to turn it off for the project that holds the OnLink service account.
What else can I bring in? Anything Cloud Asset Inventory lists. Change assetTypes to cloudresourcemanager.googleapis.com/Project for projects, container.googleapis.com/Cluster for GKE clusters, sqladmin.googleapis.com/Instance for Cloud SQL, or storage.googleapis.com/Bucket for buckets.